
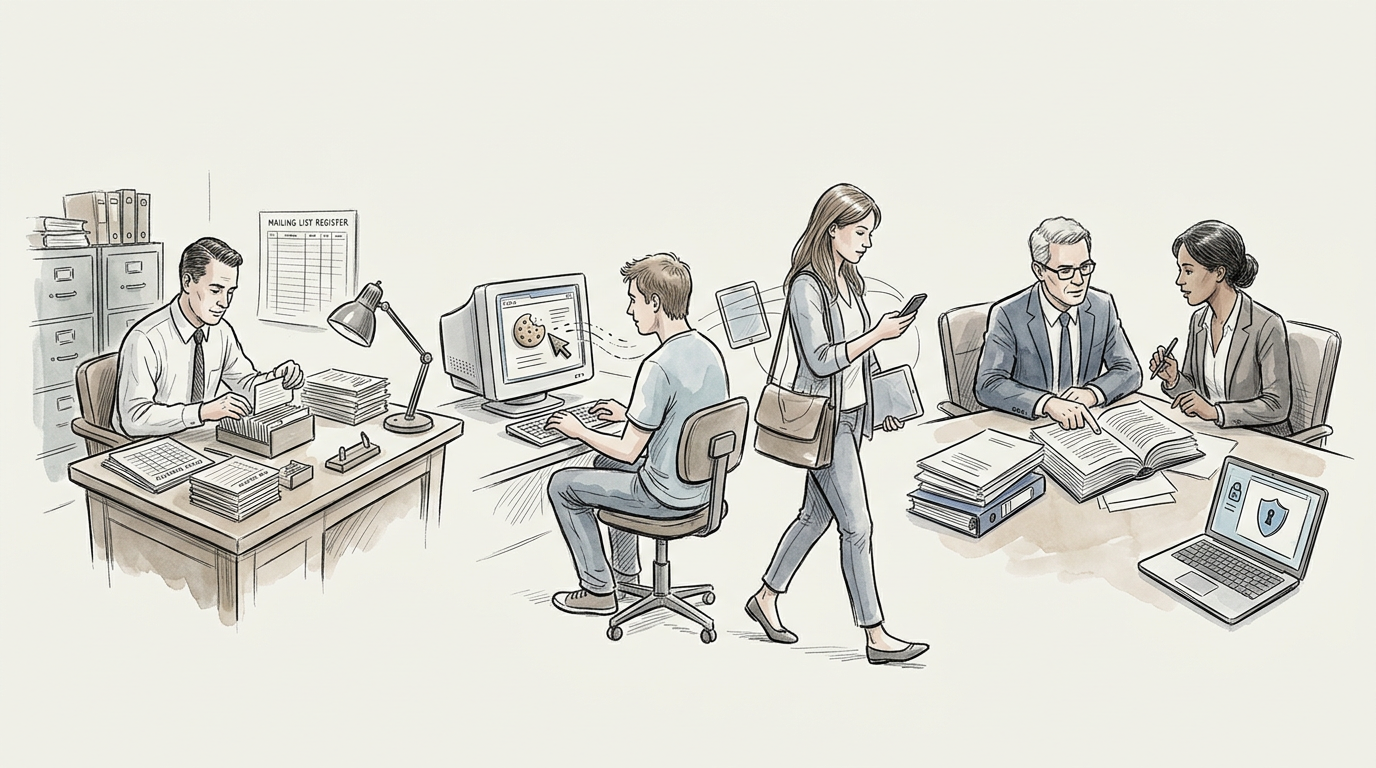
Advertising has always depended on information about audiences. What changed in the late twentieth and early twenty-first centuries was the scale, granularity, and persistence of that information. As advertising moved from broad demographic assumptions toward individually addressable data systems, a new privacy debate emerged around the industry itself. Database marketing, web cookies, behavioral targeting, mobile identifiers, and platform data did not simply improve media efficiency. They altered how advertisers defined audiences, how agencies and intermediaries bought media, how consumers were observed, and how regulators understood the line between legitimate commercial practice and surveillance.
That history matters because the current privacy landscape was not created by a single technology or scandal. It developed through a series of professional and technical shifts in advertising practice. Each new tool promised more relevance, less waste, and better accountability. Each also expanded the industry’s ability to collect and connect data across contexts that consumers often did not fully understand. The resulting debate reshaped regulation, platform governance, media economics, and public trust.
Before Digital Tracking: Direct Marketing and the Rise of the Customer Record
Long before the web, advertisers were building systems to identify likely buyers more precisely than mass media alone could allow. Nineteenth-century mail-order firms relied on customer lists, subscription records, and merchant files. By the early twentieth century, direct mail had become a specialized discipline, supported by list brokers, circulation audits, and increasingly sophisticated segmentation. What distinguished later database marketing was not the basic idea of addressability, but the computational ability to store, update, score, and merge large volumes of customer information.
By the 1960s and 1970s, improvements in computing made customer files more central to advertising and sales planning. Credit bureaus, catalog marketers, publishers, and retailers all accumulated records that could be used to model likely response. The modern direct marketing field professionalized around these capabilities. Industry groups such as the Direct Mail Advertising Association, which later became the Direct Marketing Association, promoted data-driven targeting as more accountable than mass advertising.
A key transition came in the 1980s, when “database marketing” became a recognized term of art. Practitioners such as Robert D. “Bob” Kestnbaum are often credited with helping formalize the field, though the practice drew on broader developments in direct response, loyalty programs, and customer relationship management. Database marketing combined transaction histories, demographics, geographic information, and response models to guide prospecting and retention. Retailers, financial services firms, airlines, and catalog companies used these systems to decide who should receive which offer, when, and through what channel.
The business appeal was obvious. Instead of buying only generalized audiences from media owners, marketers could increasingly organize communications around named or identifiable customers. Yet the privacy implications were already visible. As personal data moved through list rental, cooperative databases, and append services, consumers often had little visibility into how information about them was being exchanged. Public concern over computerized records had been building since at least the early 1970s, when the U.S. Department of Health, Education, and Welfare’s 1973 report Records, Computers, and the Rights of Citizens articulated Fair Information Practice principles that would influence later privacy law and policy. Advertising was not the only issue, but targeted commercial use of personal data was part of the broader shift.
From Browser Function to Advertising Infrastructure
The web introduced a different data environment. Early web advertising in the mid-1990s was relatively blunt. The first widely recognized banner ad, sold by HotWired in 1994, was bought against a publication’s audience rather than against an elaborate user profile. But the web’s architecture also made it possible to monitor activity in ways that print and broadcast never could.
The browser cookie became one of the central tools. Netscape introduced cookies in 1994 as a technical mechanism to help websites remember stateful information, such as logins or shopping cart contents. Lou Montulli, a Netscape engineer, is widely associated with the implementation. Cookies were not originally created as an advertising technology. They became one because they allowed websites, ad servers, and third parties to recognize a browser over time.
That distinction between first-party and third-party use became historically important. A first-party cookie generally allowed a site to remember its own visitors. A third-party cookie, set through external ad-serving or embedded content, allowed another company to recognize the same browser across multiple sites. For advertisers and agencies seeking frequency control, sequencing, measurement, and audience segmentation, this was a breakthrough. For privacy advocates, it was the beginning of a system in which people could be tracked across the web without meaningful comprehension.
In 1996, the U.S. Federal Trade Commission held a workshop titled “Consumer Privacy on the Global Information Infrastructure,” one of the early federal signs that online commercial data practices were becoming a regulatory issue. By the late 1990s, the FTC was repeatedly examining online profiling, notice, consent, and self-regulation. The agency’s reports from that period show that concern over online privacy was already tied to advertising-supported business models, not merely to abstract fears about technology.
The DoubleClick Moment and the First Major Web Privacy Shock
No company better symbolizes the first major collision between ad-tech targeting and privacy debate than DoubleClick. Founded in 1996, DoubleClick helped professionalize ad serving and campaign management for web publishers and advertisers. Its tools improved delivery, measurement, and targeting in an online media market that was still relatively immature. In practical advertising terms, DoubleClick helped move web display from static placement buying toward data-enabled campaign management.
The controversy deepened when DoubleClick announced in 1999 that it would acquire Abacus Direct, a major direct marketing data company whose cooperative database contained catalog and retail purchase information. Privacy critics and regulators immediately focused on the prospect of linking anonymous or pseudonymous online browsing data with offline personally identifiable consumer records. DoubleClick stated that it had no immediate plan to merge names with web surfing profiles in the way critics feared, and the company later retreated from the proposed integration under public and regulatory pressure. Still, the episode was pivotal. It made visible a possibility that had been implicit in digital advertising all along: the fusion of media exposure data with broader consumer dossiers.
The FTC investigated aspects of DoubleClick’s data practices, and although the Commission closed the investigation in 2001 without taking action on the Abacus issue, the case had lasting effects. It showed that targeting technology could quickly trigger backlash when the industry moved faster than public expectations. It also demonstrated that data practices once considered operational or technical could become reputational and political liabilities.
This period also saw the Network Advertising Initiative take shape. The NAI emerged in 2000 as an industry effort by major online ad companies to establish self-regulatory principles around notice, choice, access, and security for online profiling. Self-regulation had long been a familiar advertising response to criticism, but online behavioral tracking tested its credibility. The core professional question was whether the industry could set rules strong enough to preserve public trust while protecting a fast-growing data-driven business model.
Behavioral Targeting Moves Into the Mainstream
In the 2000s, behavioral targeting evolved from a specialized capability into a standard part of digital advertising strategy. Search advertising, led by companies such as Google after the launch of AdWords in 2000, already linked commercial messages to user intent in ways that were highly valuable to advertisers. Display advertising followed a more complicated path, because browsing behavior had to be inferred, categorized, and operationalized through cookies, page context, referrer data, and later a host of data management tools.
A number of ad-tech firms helped build this infrastructure. Tacoda, founded in 2001, was one of the more visible behavioral targeting companies in display advertising and was acquired by AOL in 2007. Revenue Science, BlueKai, Quantcast, 24/7 Real Media, and many others contributed to the growing market in audience segmentation, exchange-based buying, and data onboarding. These firms did not merely sell technology. They helped redefine inventory from pages and placements into audiences and probabilities.
For agencies and marketers, this changed professional practice in several ways. Media planning became more dependent on data science, tagging, attribution, and audience modeling. Campaigns could be optimized in flight. Retargeting made it possible to reach users who had visited a product page but had not converted. Data management platforms later allowed brands to combine first-party customer records with third-party audience data and media activation tools.
At the same time, the privacy stakes expanded. Cross-site tracking meant that many consumers were being observed through chains of intermediaries they had never heard of. Data collection was no longer confined to the publisher they were visiting or the brand they were considering. It was distributed across ad servers, exchanges, analytics providers, data brokers, demand-side platforms, and verification vendors. The advertising supply chain had become, from a privacy perspective, difficult to see and difficult to explain.
Public concern intensified as journalists and advocates exposed how pervasive that tracking had become. The Wall Street Journal’s “What They Know” series, launched in 2010, played an important role in showing broad audiences the extent of commercial web tracking. Academic researchers also documented the reach of third-party trackers across the web. These findings mattered because they translated a technical industry practice into a consumer-facing story about observation, profiling, and loss of control.
Self-Regulation, “Do Not Track,” and the Limits of Notice and Choice
As behavioral advertising grew, the industry expanded its self-regulatory architecture. In the United States, the Digital Advertising Alliance launched the AdChoices program in 2010, building on principles developed by major trade groups. The program aimed to give consumers notice of interest-based advertising and a degree of control through opt-out tools associated with the familiar triangular icon.
From an industry standpoint, this was a significant effort to standardize disclosure and reduce pressure for stricter regulation. It reflected a long-standing belief that advertising could preserve flexibility through self-governance if it offered transparency and reasonable consumer choice. Yet critics argued that the system depended too heavily on users understanding technical distinctions, clearing cookies, navigating fragmented opt-outs, and accepting tracking by default.
Browser-based “Do Not Track” proposals highlighted those tensions. The idea gained momentum around 2010 and led to technical and policy work through the World Wide Web Consortium and other forums. Major browser makers, including Mozilla and Microsoft, supported some form of user signal intended to communicate a preference not to be tracked. But the standard never produced a universally binding industry response. Disagreement over definitions, compliance, business incentives, and enforcement limited its practical effect.
The failure of Do Not Track was historically revealing. It suggested that targeted advertising had become too structurally important to digital media economics for voluntary restraint to emerge easily. Publishers needed ad revenue. Platforms and intermediaries were competing on data capability. Advertisers wanted measurable performance. In that environment, privacy protections that threatened addressability and attribution faced strong resistance unless required by law, imposed by browsers or operating systems, or demanded by consumers at scale.
Mobile Advertising and the Expansion of Identity
The shift from desktop browsing to mobile devices did not end targeted advertising. It broadened it. Smartphones created new streams of commercially valuable data, including app usage, device characteristics, and location information. Because cookies worked inconsistently in mobile app environments, platform-controlled identifiers became especially important.
Apple’s Identifier for Advertisers, or IDFA, was introduced in 2012 as part of iOS 6. Google Play services later offered the Android Advertising ID. These identifiers gave advertisers and ad-tech firms a standardized way to recognize devices for targeting, attribution, and measurement while nominally separating advertising use from more permanent hardware identifiers. In practice, they extended addressability into mobile ecosystems that were deeply personal and frequently carried everywhere.
Location data intensified the privacy debate. Mobile advertising could use precise or approximate geographic signals for store visitation analysis, local targeting, and audience segmentation based on habitual movement patterns. That commercial potential attracted extensive participation from SDK providers, app developers, exchanges, and data brokers. It also raised concerns that many users had little idea how granular location collection had become or how widely it could circulate in the data economy.
Regulators took notice. In 2013, the FTC released a staff report on mobile privacy disclosures, emphasizing the complexity of the mobile ecosystem and the need for clearer information. Enforcement actions over deceptive privacy claims, undisclosed data sharing, and weak data security increasingly touched companies operating in digital advertising and adjacent sectors. The mobile era made one point unmistakable: targeted advertising was no longer just about web pages and browser files. It was becoming part of a larger identity and behavioral data infrastructure spanning devices, apps, and offline movement.
Platform Data and the Consolidation of Advertising Power
As privacy debates over third-party tracking intensified, another model of targeting grew even more powerful: platform-based advertising rooted in logged-in user relationships. Companies such as Google, Meta, Amazon, and others did not depend solely on cross-site cookies to infer audiences. They could draw on search histories, social graphs, engagement data, commerce signals, video viewing, app activity, and other first-party or platform-controlled information generated within their ecosystems.
This changed the structure of advertising markets. The major platforms offered scale, identity persistence, closed measurement systems, and increasingly sophisticated optimization. Their data advantages made them highly attractive to advertisers seeking performance and reach. At the same time, their prominence complicated the privacy conversation. Some public debate focused on ad-tech intermediaries and invisible third-party tracking, but large platforms were assembling extraordinarily rich audience models from logged-in environments where users had ongoing, if often imperfectly understood, relationships with the service.
The Cambridge Analytica scandal in 2018 did not primarily concern targeted advertising mechanics alone, but it intensified public scrutiny of platform data collection and downstream use. It reinforced a broader realization that digital platforms had accumulated vast information resources that could be used not just for commercial targeting, but also for political messaging, profiling, and influence operations. For advertising history, the episode is significant because it expanded privacy concerns beyond banner tracking into a wider critique of platform surveillance and data governance.
Platform dominance also affected professional advertising practice. Brands and agencies increasingly built strategies around “walled gardens,” where campaign execution and measurement took place inside systems controlled by the media seller. That arrangement offered precision and convenience, but it also reduced independent visibility into data flows and performance verification. Privacy and competition debates therefore became intertwined. Questions about who had the data, who could use it, and who could audit it were no longer just technical concerns. They were core issues in the economics of modern advertising.
Regulation Catches Up, Unevenly
The privacy debate around targeted advertising has never been shaped by the United States alone. European policy, in particular, played a central role. The European Union’s 1995 Data Protection Directive established a foundational framework for personal data processing. The 2002 ePrivacy Directive, later amended in 2009, addressed electronic communications and helped create the legal basis for consent requirements around cookies and similar technologies in Europe. The often-criticized cookie banner is one visible consequence of that legal history.
The General Data Protection Regulation, effective in 2018, marked a major turning point. GDPR imposed stricter requirements for lawful processing, consent in some contexts, data subject rights, accountability, and significant penalties. For targeted advertising, it challenged industry assumptions about passive notice, broad downstream sharing, and opaque vendor chains. Although implementation and enforcement have varied, GDPR changed compliance practices globally because many multinational advertisers, publishers, and technology firms could not treat Europe as an isolated case.
In the United States, privacy regulation has been more sectoral and fragmented. The Children’s Online Privacy Protection Act of 1998, effective in 2000, directly affected digital advertising involving children under 13. FTC enforcement under Section 5 of the FTC Act targeted unfair or deceptive privacy and data security practices. State law later became more important, especially with the California Consumer Privacy Act of 2018 and the California Privacy Rights Act of 2020. These laws gave residents rights related to access, deletion, and certain forms of data sharing or selling, with clear implications for advertising technology.
What regulation changed most was not the existence of targeting, but the compliance burden and legitimacy assumptions surrounding it. Data collection that had once been treated as a routine operational feature of digital advertising now required legal review, consent management, contractual controls, and governance structures. Privacy moved from the margins of media operations into the center of advertising risk management.
The Browser and Operating System Strike Back
A striking feature of this history is that some of the most consequential privacy changes came not first from legislatures, but from technology gatekeepers. Browser makers and operating system providers increasingly intervened in tracking practices they regarded as excessive or misaligned with user expectations.
Apple’s Safari introduced Intelligent Tracking Prevention in 2017, using machine learning and other methods to limit cross-site tracking. Mozilla’s Firefox later expanded Enhanced Tracking Protection. Google announced in 2020 that Chrome would phase out support for third-party cookies, though the company’s path and timeline shifted repeatedly amid industry and regulatory scrutiny. Regardless of the final implementation, the direction of travel was clear: browser-level controls were reducing the durability of one of digital advertising’s foundational targeting tools.
Apple’s AppTrackingTransparency framework, rolled out in 2021, had especially visible consequences. Apps seeking to track users across apps and websites owned by other companies had to obtain permission through a standardized prompt. Opt-in rates were far lower than many ad-tech firms had hoped, disrupting mobile measurement, retargeting, and audience matching. The policy did not end targeted advertising, but it altered who could do it effectively and on what terms. Large platforms with extensive first-party data were often better positioned than smaller intermediaries dependent on shared identifiers.
This phase of the privacy debate was historically significant because it showed that infrastructure owners could reset advertising norms faster than many formal policy processes. It also revealed a recurring pattern in advertising history: when a medium’s dominant commercial practices generate enough distrust or concentration risk, control often shifts toward those who own key distribution or access points.
Why the Debate Became So Persistent
The privacy debate around targeted advertising has endured because it is not really about one single objection. It combines several different concerns that overlap but are not identical.
One concern is informational. Consumers often do not know what data is collected, who receives it, or how long it persists. Another is dignitary. People may object not simply to being advertised to, but to being watched, inferred, categorized, and acted upon without meaningful participation. A third is economic. Publishers, platforms, data brokers, and advertisers all derive value from information asymmetries that users rarely negotiate on equal terms. A fourth is political and social. Systems built for commercial targeting can also shape public discourse, pricing, credit, employment advertising, and exposure to opportunity.
Advertising professionals have not always experienced these concerns as equally central. Many practitioners viewed targeted advertising primarily through the lens of efficiency, relevance, and return on investment. And there is evidence that better targeting can reduce waste and improve campaign performance in certain contexts. But the industry’s own success in making targeting more precise is what made privacy debate unavoidable. The more advertising could follow people, connect their actions across environments, and optimize messages based on inferred behavior, the less plausible it became to describe data collection as incidental to media delivery.
What Changed in Advertising Practice
From a historical perspective, the development of targeted advertising changed the profession in at least five lasting ways.
First, audience definition shifted from broad categories toward dynamic, data-derived segments and eventually toward individual-level probabilistic decisioning. Media planning became inseparable from data architecture.
Second, measurement and targeting converged. The same systems used to count impressions and conversions increasingly helped determine who would be reached next. This gave advertising unprecedented feedback loops, but also expanded surveillance incentives.
Third, the number of actors involved in campaign delivery multiplied. Agencies, publishers, advertisers, ad servers, exchanges, SSPs, DSPs, DMPs, CDPs, clean rooms, and identity providers all entered the workflow. Privacy risk spread through this chain.
Fourth, first-party data became strategically central. As third-party identifiers came under pressure, marketers invested more heavily in loyalty systems, CRM integration, consented customer relationships, retail media networks, and authenticated environments.
Fifth, privacy itself became a professional competency. Legal, policy, data governance, and ethics teams moved closer to media and marketing operations. Compliance was no longer peripheral to campaign execution.
The Historical Legacy of Targeted Advertising
The privacy debate created by targeted advertising was not a temporary reaction to novelty. It was the consequence of a deep structural transformation in advertising from message distribution toward continuous data extraction and audience management. Database marketing introduced the logic of the customer record. Cookies and ad serving extended recognition across web sessions. Behavioral targeting and cross-site tracking turned browsing activity into tradable advertising intelligence. Mobile identifiers and location data moved that intelligence into personal devices and physical space. Platform data consolidated targeting power inside large digital ecosystems.
At each stage, the industry advanced a compelling professional rationale: more relevant messages, better performance, less wasted media, more accountable spending. Those arguments helped make targeted advertising indispensable to modern media economics. They did not resolve the underlying question of how much observation advertising should require.
That question now shapes the future of the field. Current debates over consent, data minimization, retail media, clean rooms, connected television identifiers, AI-driven audience modeling, and synthetic measurement are all descendants of the earlier history. Modern advertising professionals operate in a marketplace built by targeting, but also constrained by the distrust targeting helped create.
Understanding that history clarifies what changed. Privacy did not suddenly become relevant to advertising in the platform era. It became unavoidable when advertising acquired the technical means to remember, connect, predict, and personalize at scale. Once that happened, privacy ceased to be merely a legal issue at the edge of practice. It became one of the central historical questions of advertising’s data-driven age.
Leave a Reply